Elaris Core sits between the systems you already run and the partners you need to reach.
Data arrives in whatever shape its source produces. We validate the message for structural integrity
and semantic conformance. Your data is sent, in compliance with your approved, tailored disclosure policy,
to all of your mission partners, in the exact configuration they individually require.
The Elaris Platform — Driving Data Advantage!
CJADC2Combined Joint All-Domain Command and Control. Joint means across US services; Combined means with allied and partner nations. The C was added because no recent conflict — and no serious exercise — is US-only.
adds one letter to JADC2, and that letter carries most of the difficulty.
Joint is hard but tractable: shared classification, shared doctrine, one
acquisition authority, and someone who can ultimately mandate a standard.
Combined has none of those. Separate nations, separate data classification
policies, separate releasability rules, and legacy systems which were never
designed to interoperate.
That problem, is why the Elaris Platform exists. We are your data interoperability
layer where datasets become available between each partner, in the exact shape
required, and released only under the disclosure policy you set.
If data must cross a national boundary, “can we send this?” becomes a policy question. “are we permitted to — to this recipient, in this form, right now?”
The heart of the Elaris suite of capabilities, the Core node seamlessly ingests your data and processes each message through a secure pipeline. Automatically validate data integrity using Elaris Schema Registry and ensure semantic conformance to your own tailored business and disclosure policies using the Elaris Disclosure and Data Policy Manager.
Spin up an Elaris Core or Edge Node in minutes, not days!
Edge relays data to your Core node — it is the same Elaris platform, deployed forward.
Push an Edge node into your DMZ, a commercial cloud, or an austere site with minimal hardware
resources. The Edge node will relay data into your Core over modernized encryption. One platform
to accredit, patch, and one your operators already know how to run
and manage.
Deploy it wherever the mission requires!
Your data comes in different formats and from a multitude structured and unstructured sources.
Rapidly derive, create, manage and store each of your data schemas in a centralized, immutable
registry, giving you a single-source of truth!
Harness the flexibility to rapidly evolve your data schemas as operational needs demand.
Information sharing requirements vary mission-to-mission. Easily tailor your
data feeds so that your partners see the information your policies permit!
Conditionally tailor your information pipelines to standardize outputs, reduce spillages and eliminate human errors.
Illuminate your Information Exchange (IER) flows with a visual geospatial map! Detect data delivery
problems in real time and monitor the health of your global information sharing architecture.
Visualize your information flows in realtime, using your existing data COP!
Digitize your Security Classification Guides (SCG) and Data Owners Guide (DOG) to gain control over
your information dissemination policies and workflows!
The Elaris Data Policy Manager gives you granular, conditional logic application
and enforcement control across your entire schema registry.
Elaris Data Policy Manager gives you the clarity to know that your data is
well prepared before it reaches the CDS!
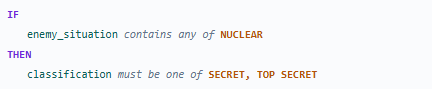 Shown for illustration only. All data, names and configurations depicted are notional and do not represent real operational information.
Manage information sharing and disclosure approvals at granular levels.
No destination (internal or external) receives data until a Disclosure
Officer authorizes the data flow.
Approve or Revoke
dissemination for a single partner, country or an entire schema!
An explicit and revocable approval gate between data in and data out ensures that...
Disclosure Officers always have full control over information release!
 Shown for illustration only. All data, names and configurations depicted are notional and do not represent real operational information.
Streamline the design of your data sharing requirements on a drag-and-drop canvas and sketch out every data flow before you build it! Your data flow architecture should be well understood prior to implementation, exercise or conflict.
Rapidly prepare for exercises and real-world events with the Elaris Mission Planner!
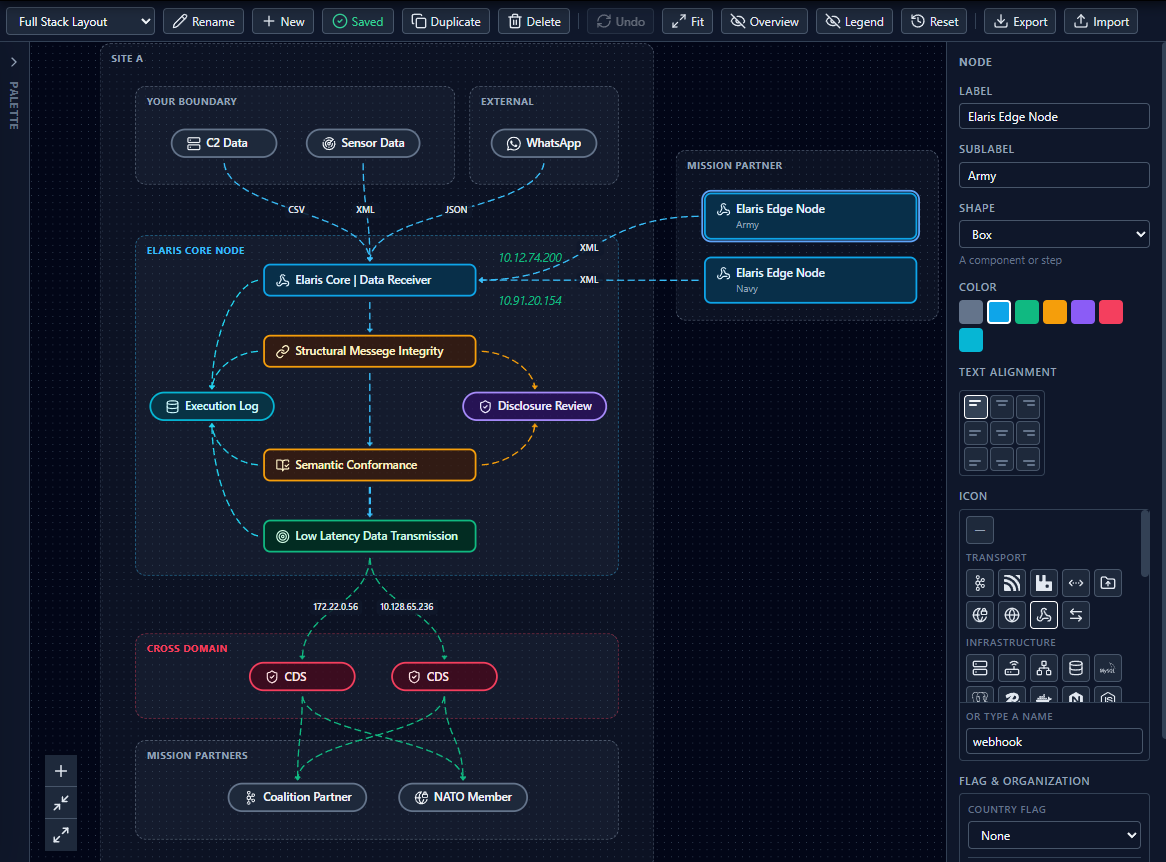 Shown for illustration only. All data, names and configurations depicted are notional and do not represent real operational information.
Our secure data pipeline supports 132 configuration variations to meet nearly any demand.
Share data the way your operational needs demand. We work hard
to ensure that you are never limited in your ability to share data with your mission partners!
Let's talk about your unique objectives!
104 hash-chained audit events covering all configuration and security-relevant events. Forward to your existing SIEM using
syslog UDP, TCP or TLS (certificate-based) protocols.
Subscribe to only the Elaris events your role requires!
Deploys as a self-contained stack with no external dependencies. Purpose built
for disconnected environments, not retrofitted for them.
Zero external dependencies; Cloud readiness from day 1!
Note: product screenshots on this page are shown for illustration only. All data, names and configurations depicted are notional and do not represent real operational information.
The DoD’s data strategy sets seven goals for the data itself — known collectively as VAULTIS. They are properties of your data holdings, not features of any product, and meeting them is a program responsibility spanning governance, policy, staffing and funding.
| VAULTIS Goal | What it means for your data | What Elaris contributes |
|---|---|---|
| Visible | Consumers can discover that a dataset exists and where to obtain it. | Every schema in use is registered, versioned and inspectable in one place, so what you exchange is documented rather than tribal knowledge. |
| Accessible | Those authorized to have the data can actually retrieve it. | Data ingest and delivery using modern protocols and also the legacy protocols your partners may rely on. |
| Understandable | A consumer knows what a field means, not merely what it is called. | Field-level mappings are declared once, reviewed, and applied identically to every message thereafter — so meaning is not re-derived per integration. |
| Linked | Data relates across sources, so it can be joined rather than read in isolation. | Common target schemas across data feeds, so records arrive on shared field definitions instead of per-source vocabularies. |
| Trustworthy | Consumers can rely on the data — its integrity, its provenance, its handling. | Structural and semantic validation on every message, and a hash-chained audit record of what was sent, to whom, and on whose authority. |
| Interoperable | Common formats and standards, so exchange does not need bespoke work each time. | One canonical core between systems and standards, so onboarding a partner is a configuration, rather than an integration project. |
| Secure | Data is protected and released only to those cleared and authorized for it. | Your disclosure policy enforced at the gate, per destination, with release authorized by a named officer and revocable at any time. |
Goals as stated in the DoD Data Strategy. Elaris is a commercial product, not a DoD program of record, and no endorsement is implied. Meeting these goals is a program responsibility; the right-hand column describes what the platform contributes, not compliance it confers.